An open directory was found on a server at 104.233.217[.]108, serving its contents over port
8888. The listing ran to 64,006 files. Among them sat the source code, PHP and Python
backends, admin modules, delivery routers and operator notes for two iOS exploit kits that
public reporting had named only days earlier: Coruna and DarkSword. None of it had
been cleaned up.
At first glance this looked like the campaign's live infrastructure. Reading the files says
otherwise. The addresses public reporting tied to the attack, the injector domains, the random
.icu routers, the telemetry channel codes, do not appear anywhere in this directory. What is
here is the workbench: the kit being parsed, cloned, rebuilt and offered as a service, with its
own set of panel addresses that the public indicators never mentioned.
At a glance
- The open directory on
104.233.217[.]108sits in AS54600, PEG TECH INC, United States, on port 8888, first seen by Etugen around September 24, 2026 and last seen around November 2, 2026. Etugen Trashpile classified the listing across 22 categories, fromcredential-accessandexposed-secretstoc2,loader,miner,webshellandactive-directory. - The directory holds the backend of both kits:
CorunaParse.php,DarkSword.php,darksword_router.py, and a Python management layer bannered asiOS V2 管理系统. - The most significant finding is panel infrastructure absent from the incident's public
indicators:
we.xpjkk[.]xyzresolving to43.247.132[.]175, andi.131422[.]comnamed in the router as the source the attack chain was captured from. - The collection modules target crypto wallet seed phrases, user notes and photo albums,
wrapping the albums into 7z archives protected by a
MASTER_KEYpassword. - The incident's payload, collected by Etugen from
136.113.106[.]136on November 17, shares two kit-specific artifacts with this workbench: the attributedata-chain-urland the stage directoryweifile. The iOS stage of the incident was built with this kit family. - The injection-side indicators from public reporting,
1688360[.]cc,webshell[.]lol, the.icurouters, the channel code02111110,BIGNIAOand/api/iptj, do not appear in the directory's content. The stringJIUJIU888matched ten files, but only as an account name in records about an unrelated fraud operation, not as the loader path. - Stealer log records hold eight credential records for
chat.webshell[.]lolandxiaoshen.webshell[.]lol, the oldest dated April 13, 2026. The injector domain was in use five months before its first reported appearance. - Dated backups place edits on October 9, 2026, and an operator pentest report inside the directory is dated September 21, 2026, pointing at a workbench that has been maintained for weeks.
Background
A public report published on November 16, 2026 described a supply-chain incident in which
malicious JavaScript was served through a web experimentation platform to visitors of 178
organizations. On iPhones and iPads the payload loaded two iOS exploit kits, Coruna and
DarkSword, through hidden iframes. That reporting listed the injection domains, several random
.icu routers acting as iOS delivery hosts, telemetry endpoints and track.js build hashes.
This hunt started from one host that Etugen surfaced when a content search matched hundreds of
files naming those two kits, and set out to answer a single question: whose workbench is this,
and does it connect to the injection side.
The earlier injector, webshell[.]lol
The payload host was not where this actor started. Public reporting places an injector domain,
webshell[.]lol, on third-party sites from September 17, 2026, delivered through an SEO backlink
panel script, and then inside the scripts of three other third-party providers between
November 13 and 16. When the first injection through the experimentation platform was seen at
04:21 UTC on November 16, the snippet loaded webshell[.]lol/get.js. By 08:28 UTC the snippets
pointed at 1688360[.]cc/track.js instead. Public reporting calls the two the same actor's
work; the one concrete overlap it shows is that first snippet loading the older injector.
The injector is no longer serving anything. Public reporting records that the domain was placed on registry hold at 03:37 UTC on November 17, the day after the incident. The link from the injector to the payload host is therefore stated as reported, not as observed.
What stealer logs say about the domain
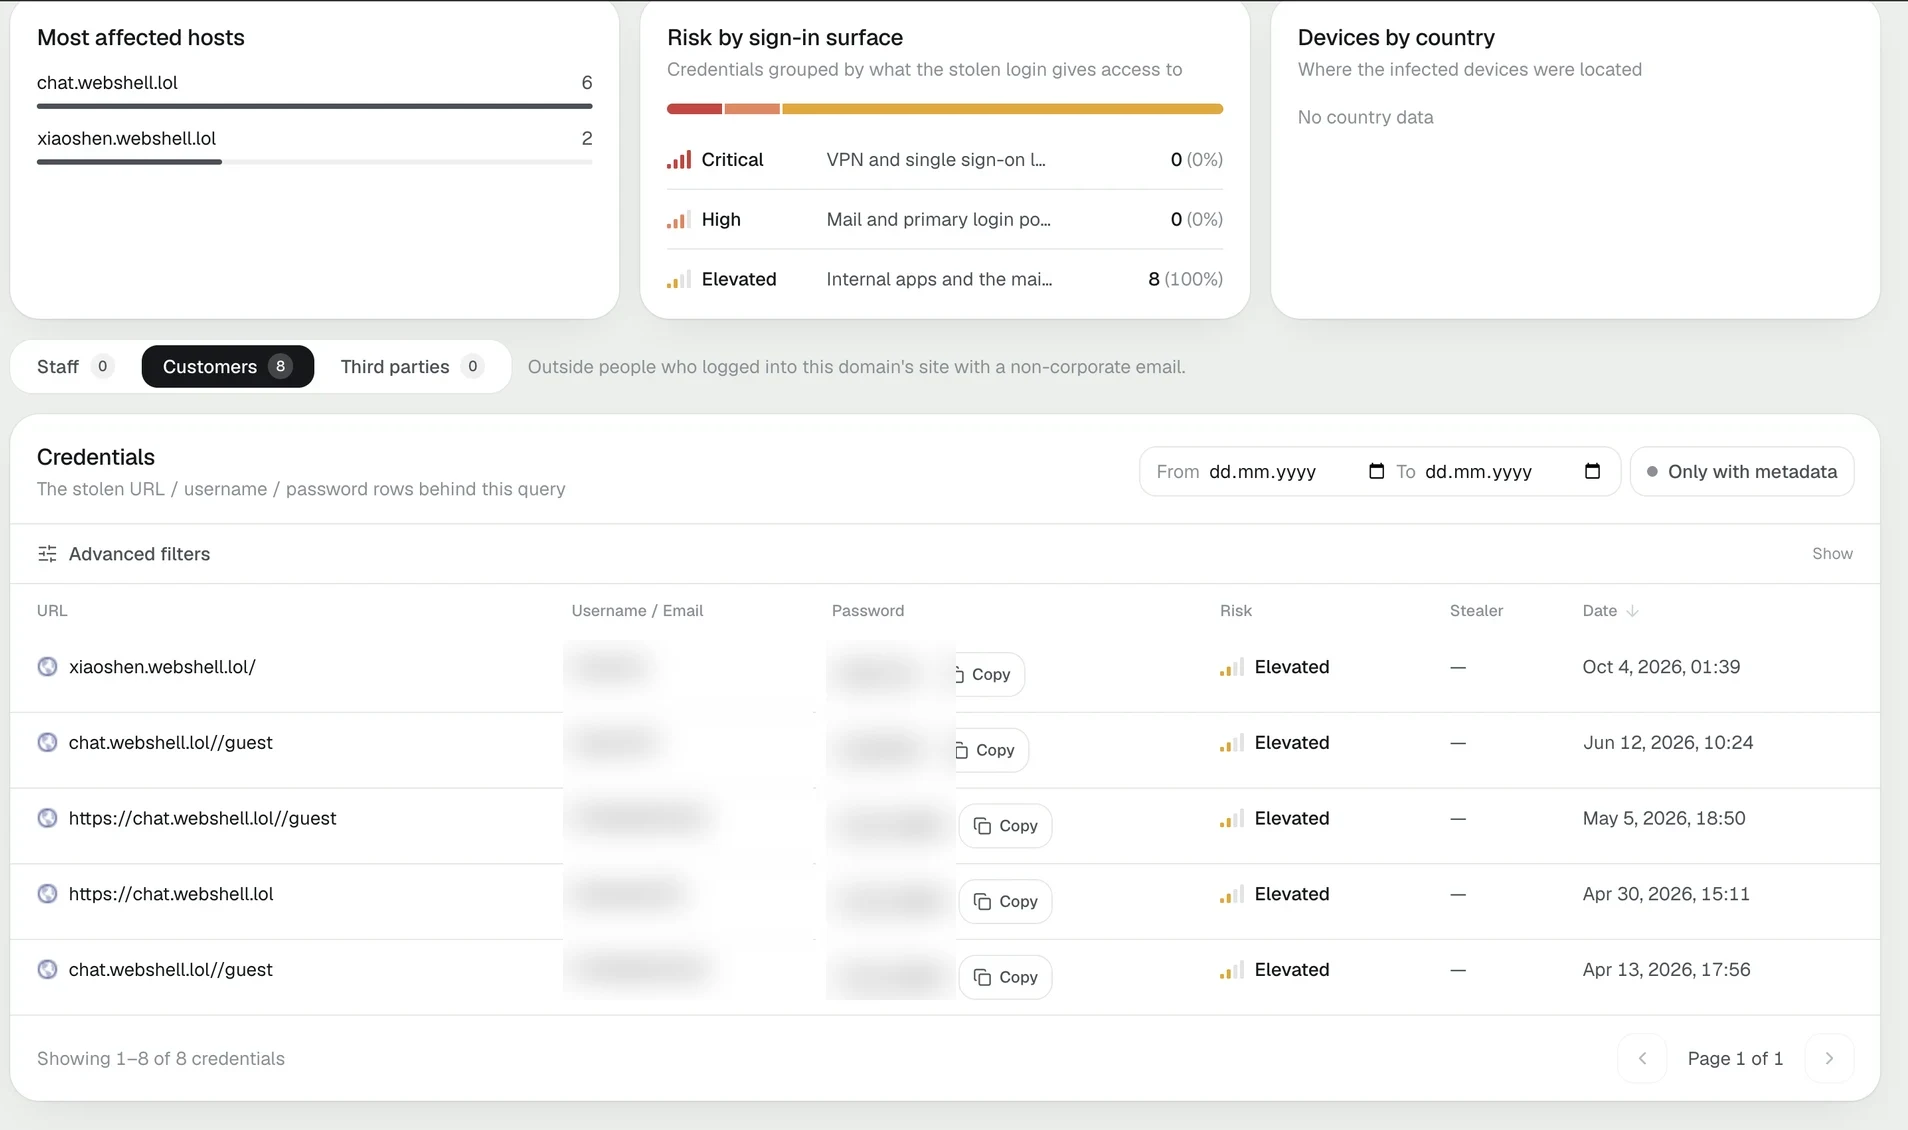
The domain has a longer history than the September date suggests. Stealer log records
reviewed during this hunt hold eight credential records for two subdomains of
webshell[.]lol, six on chat.webshell[.]lol and two on xiaoshen.webshell[.]lol. They were
saved in browsers on machines that were later infected with stealer malware. The oldest is
dated April 13, 2026, five months before the injector was first reported.
| Host | Path | Account, masked | Note |
|---|---|---|---|
chat.webshell[.]lol |
/guest |
OTH•••••212 |
Oldest record for the domain |
chat.webshell[.]lol |
/ |
das•••••312 |
Same password as the account above |
chat.webshell[.]lol |
/guest |
OTH•••••212 |
Second capture of the same account |
chat.webshell[.]lol |
/guest |
hap••••23 |
Password reused on two unrelated sites |
xiaoshen.webshell[.]lol |
/ |
Xia••••• |
Account name matches the subdomain label |
The records are enough to say three things. The domain was in use by April 2026 and carried a
chat service with a guest login at chat.webshell[.]lol, so it wasn't registered for the
November campaign. A second subdomain, xiaoshen.webshell[.]lol, takes its name from the
account recorded on it, which reads as a personal space handed to a named user. And the distinct
logins come down to four account names and three passwords: two of the names share one password
and are most likely one person.
Following the passwords
Investigating with the passwords themselves brings out more. The password shared by the two April accounts returns records on more than a dozen other sites between May and October 2026.
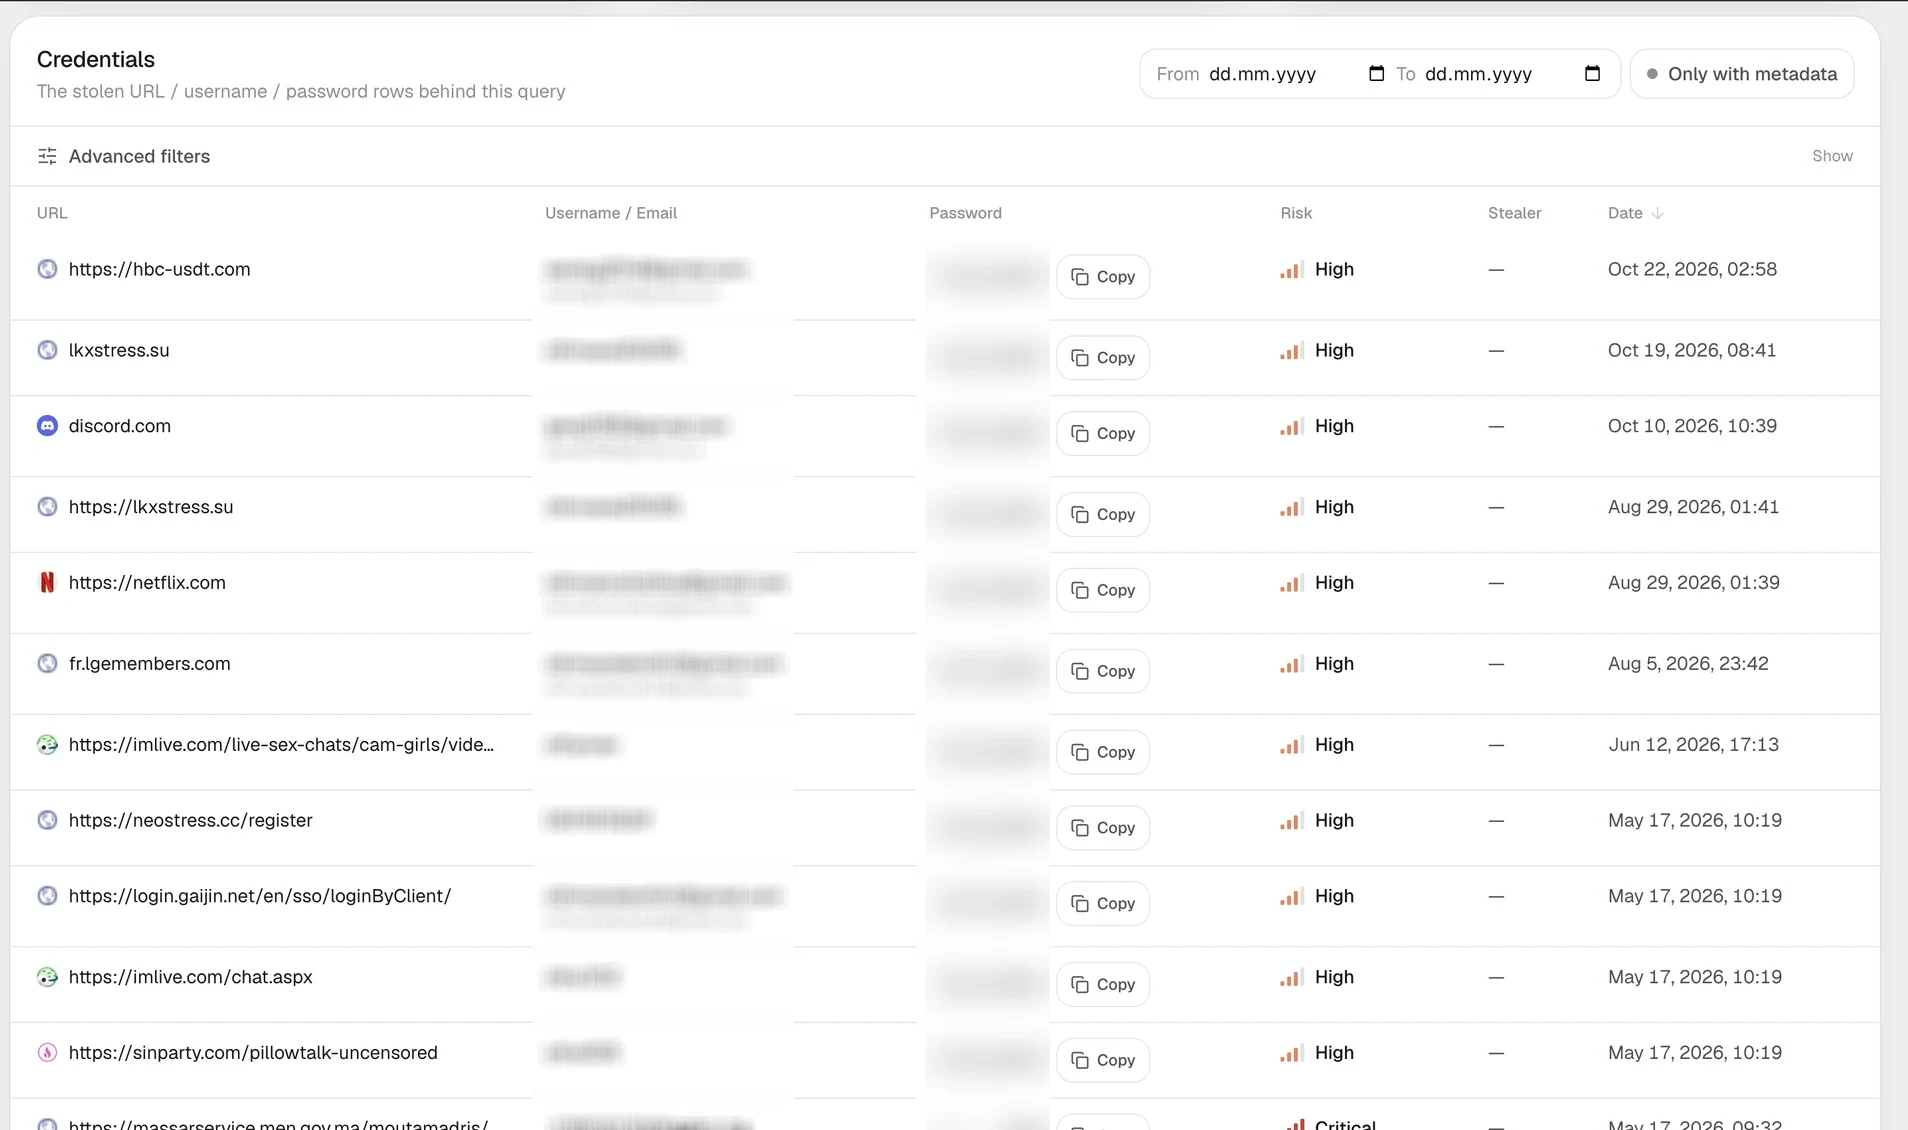
Two of those sites are DDoS-for-hire services, lkxstress[.]su and neostress[.]cc, and a
third is a USDT-themed site, hbc-usdt[.]com. The rest are everyday accounts: a chat platform,
a streaming service, a game publisher's login, adult chat sites and a Moroccan school portal.
This is the footprint of one individual, and one who registers on stresser services, not that
of a shared service account.
The password of the June account tells a different story. It returns seven matching records across three hosts.
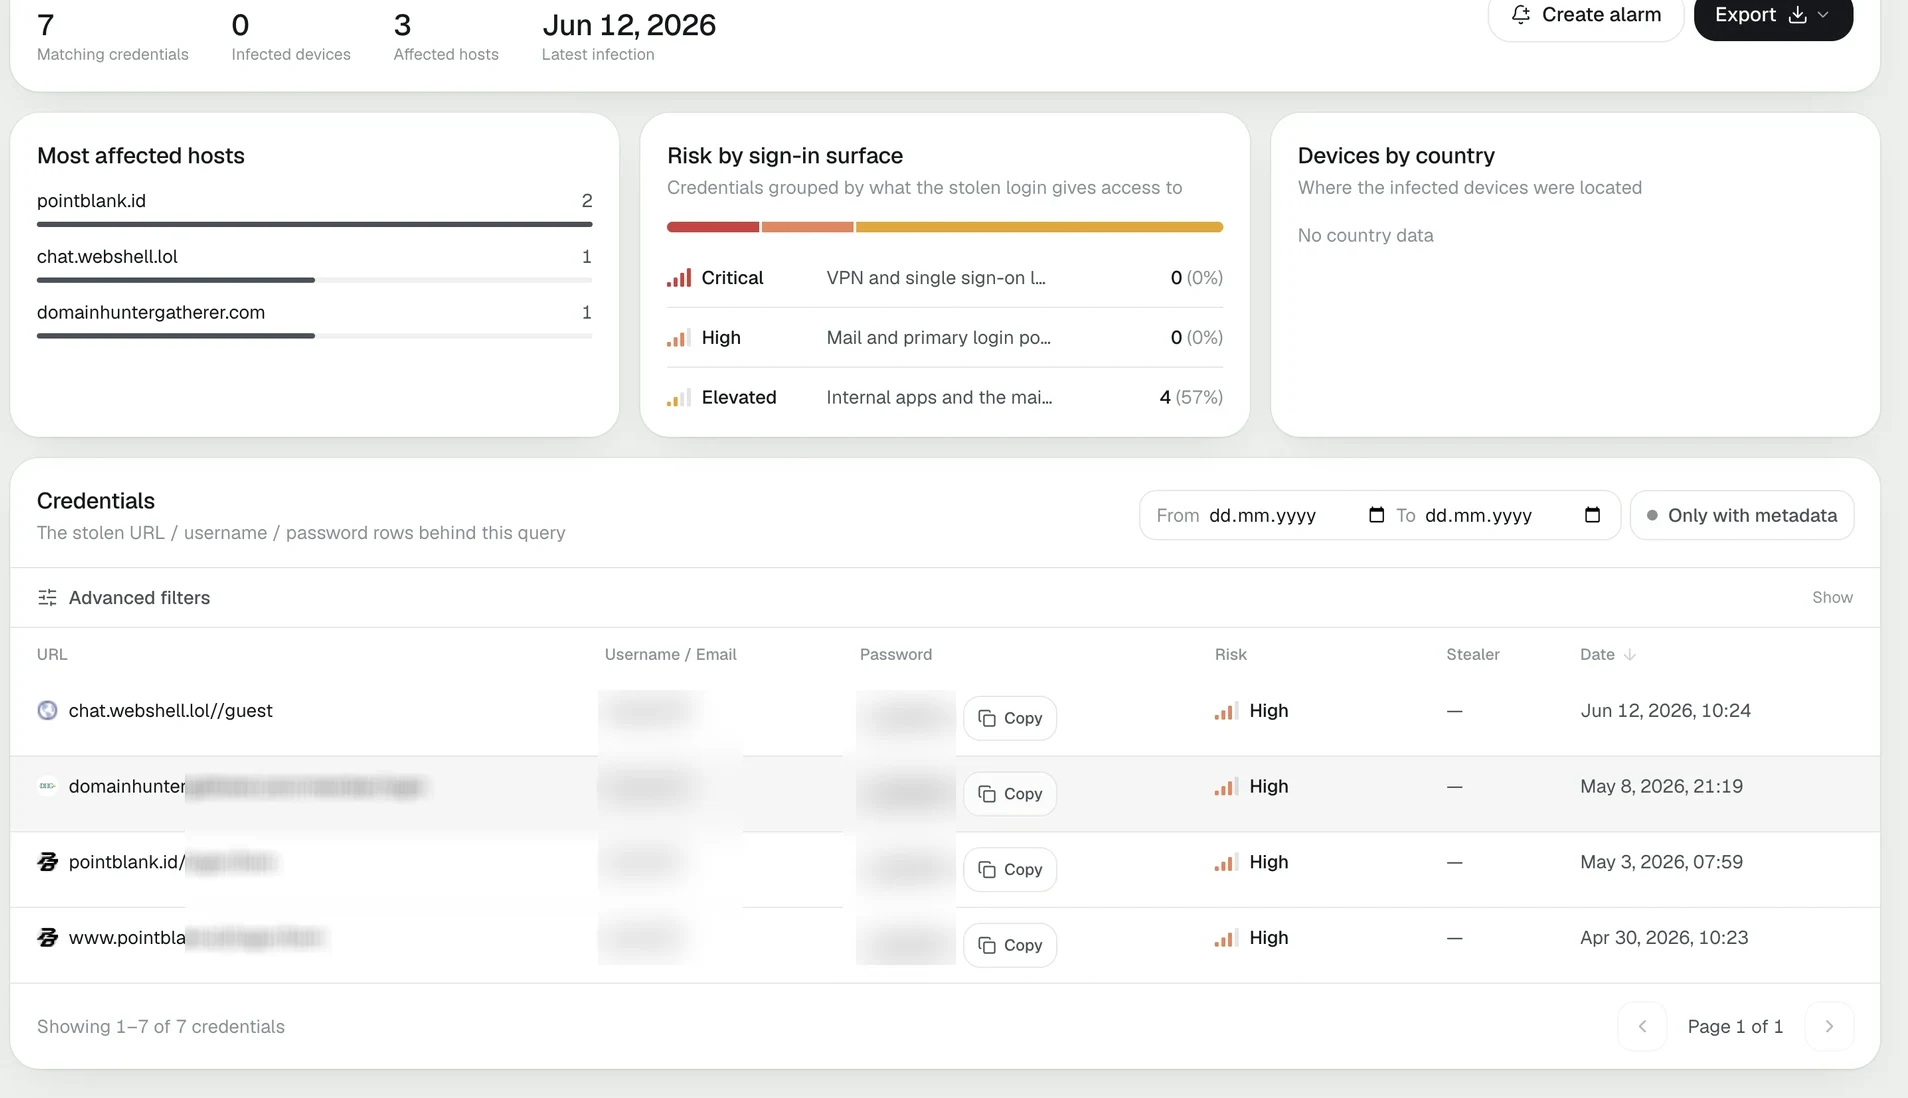
The same account name and password appear on the member login of an expired-domain research
tool, a product used in SEO and link-building work, on May 8, 2026. The same password under a
different account name appears on an Indonesian gaming portal, on April 30 and May 3. An SEO
tool account that shares a password with a chat.webshell[.]lol login is consistent with the
SEO backlink panel that public reporting names as the injector's first carrier.
It isn't proof of more than that. These records describe people who logged in to the service from infected machines. Nothing in them shows that any of these accounts operated the injector, and the records carry no stealer family name. The accounts are carried as leads at low confidence, and passwords are withheld here.
Discovery
The seed was 104.233.217[.]108. Etugen tracks it only as an open directory, not as a
classified threat host, and a full host-context lookup returned no related hosts through JARM,
certificate, malware or ASN pivots. The listing itself is what carried the investigation. The
Trashpile record assigns 22 categories and a tag set that includes certipy, amass,
mysqldump, ngrok, telegram, Webshell, Miner, Exposed:Credentials, .git/ and the
label cve-2025-63888. That CVE tag reflects content Etugen matched in the directory; its
relationship to the Coruna and DarkSword chain is not established and is left as an open
question.
| Address | Role | Open port | Service | Verification |
|---|---|---|---|---|
104.233.217[.]108 |
Open directory, kit workbench | 8888/tcp | HTTP open directory | Etugen Trashpile |
43.247.132[.]175 |
DarkSword admin panel for we.xpjkk[.]xyz |
n/a | n/a | Inferred from file contents |
i.131422[.]com |
Traffic-capture source for the attack-chain router | n/a | n/a | Inferred from file contents |
No independent port scan was run beyond the exposed 8888 listener. The two addresses in the lower rows were not scanned; they are read from the operator documents and the router header in the directory, so their role is inferred, not confirmed by a direct probe.
Inside the directory: a kit, parsed and rebuilt
The directory is not a single clean project. The same scripts appear in several copies of a backend tree, which reads as multiple snapshots of the same workspace left on disk. Two code families run through it. One is a PHP port of the kit, the other a Python management layer. A third set is operator documents and backups.
The PHP port carries the channel logic. CorunaParse.php is 28,451 B, Etugen file id
f146399d. Its header describes the Coruna channel fields /a /u /event /ub /uj /us and notes
that it is kept in sync with an admin-tree copy at admin/app/service/CorunaParse.php. It
defines a WALLET_LETTERS map that ties a single channel letter to a wallet brand, for example
a to MetaMask. DarkSword.php is 15,569 B, file id b7784dec, and describes the DarkSword
next-chain HTTP API with /api/ds/* endpoints named beacon, result and war. These two
files are the clearest fingerprint of the kit's server side.
The delivery router is Python. darksword_router.py runs to 76,465 B and maps the chain onto
three route shapes: GET /go/{code}, /pe/{filename} for DarkSword JavaScript and
/gooll/{filename} for Coruna JavaScript. Its header is where the workbench's provenance
leaks.
DarkSword 攻击链路由, iOS 18 only, 来自 i.131422[.]com 抓包
In English: "DarkSword attack-chain router, iOS 18 only, captured from i.131422[.]com." The
word 抓包 is traffic capture. The router was not written from scratch; it was reconstructed
from traffic captured against a deployment reachable at i.131422[.]com. That is the first
piece of new infrastructure the public indicators never listed.
The Python management layer
The backend scripts sit under a backend/scripts tree and share a banner.
作者: iOS V2 管理系统
In English: "author: iOS V2 management system." The same string runs across maintenance
scripts with telling names: recover_coruna_albums.py, repair_coruna_notes_sanitize.py,
audit_ios_coruna_failures.py, demote_ios18_coruna_misroute.py, coruna_sweeper.py,
brute_coruna_ts.py, merge_coruna_config_by_ip.py and demote_darksword_without_evidence.py.
These are not exploit code. They are the housekeeping of a running panel: recover albums,
sanitize notes, audit failures, demote misrouted iOS 18 victims, merge per-IP config. A kit
that only served payloads would not need them. A back-office that collects and curates victim
data would.
The application modules carry a different header, a service advertisement.
搭建 二开 网站维护 Telegram @
In English: "setup, secondary development, site maintenance," followed by a Telegram handle
that is blank in the recovered snippet. The same operator who rebuilt the router also markets
the result. Among those modules, coruna_user_set.py handles POST /api/user/set and parses
wallet mnemonic phrases while tagging the wallet source. lab_coruna_channel.py numbers
channels through a ?c= parameter, separating a main channel from agent channels.
coruna_notes_store.py stores notes through POST /api/user/avatar/pic.
coruna_chain_progress.py tracks attack-chain progress steps. coruna_bin.py is the
collection packager: it wraps a Coruna album into a 7z archive encrypted with a MASTER_KEY
password and a plaintext timestamp. Read together, the modules describe a collection pipeline
aimed at crypto wallet material, personal notes and photo albums.
The operator documents
Six documents stand out from the code. XPJKK-DARKSWORD-FULL-REPORT.md is 53,174 B, file id
9d7378ce, a Chinese-language report whose subject is a penetration test of a DarkSword admin
panel. It names the target as we.xpjkk[.]xyz, records its resolution to 43.247.132[.]175,
and labels the panel JackApple 漏洞管理后台 v9.0 with an internal code name of DarkSword
Admin. In English the panel label reads "JackApple vulnerability management backend v9.0." The
document is dated September 21, 2026.
That report reframes the whole directory. The owner was not simply running the kit. The owner
broke into, or at least studied in depth, a DarkSword admin panel operated under the handle
JackApple, then captured the attack chain from a second deployment at i.131422[.]com and
rebuilt it under a new brand, iOS V2 管理系统. The evidence leans toward a third party cloning
and reselling the kit rather than the original injection operator, though whether the two
overlap is not fully resolved.
The other documents support the picture. darksword-coruna-c2.md, 1,376 B, file id 16d679ca,
first seen September 30, 2026, holds C2 notes. coruna_c2_findings.json, file id e2255e4a,
and coruna_victim_report.json, file id e49c9b8d, are a findings file and a victim report.
darksword_passwords.txt, 684 B, file id 11d93d54, is a password list. darksword.db,
176,128 B, file id 6869b2ca, is a SQLite database. The victim report and the database are the
right place to size the collected data; they are left for an analyst to read under masking,
since counts matter and names do not.
Dated backups fix the editing in time. Three resource-fork files,
._gooll.html.bak_corunafb_20261009_031714, ._rce_loader.js.bak_corunafb_20261009_031714 and
._gooll.html.bak_coruna_fix_20261009, all carry an October 9, 2026 stamp, with one down to
03:17:14. A fork named ._DarkSword-RCE_副本, where 副本 means "copy," together with the
macOS AppleDouble forks across the tree, shows the project was copied from a Mac.
The injection side is not here
The hunt's most useful negative result is clean. The addresses, codes and endpoints that public reporting tied to the live attack were searched directly in the directory's content. None of them appear.
The searches covered the payload domain 1688360, the injector webshell.lol, the reported
domain linkforge, the fallback C2 ios-hack, the channel code 02111110, the telemetry code
BIGNIAO and the Coruna telemetry endpoint /api/iptj, each run as
ip:104.233.217[.]108 content:"<indicator>".
The pattern is consistent. Injection-stage strings are absent. The two partial matches do not
change that. JIUJIU888 appears in ten files only as an account name in records about an
unrelated fraud operation, and .icu appears in six files without any of the published router
names. This separates the workbench
from the injection infrastructure as a matter of content, not inference. A defender chasing the
November 16 incident should treat this host as a different stage of the same ecosystem, the
development and panel side, not as one of the routers that served the iframes. The two
track.js build hashes from public reporting did not match any file in the directory, which is
in line with the same split. The payload host itself is a separate record in Etugen, covered
below.
Hunting for more
The directory gives several stable patterns. Each was turned into an Etugen search a reader can run, and the new infrastructure was carried out of the files.
| Pattern | Evidence | Etugen query | Matches | Confidence |
|---|---|---|---|---|
| Coruna kit file set | CorunaParse.php, coruna_*.py |
ip:104.233.217[.]108 filename:"Coruna" |
40 | High |
| DarkSword kit file set | DarkSword.php, darksword_router.py, darksword.db |
ip:104.233.217[.]108 filename:"DarkSword" |
14 | High |
| Operator banner | iOS V2 管理系统 across backend scripts |
content:"iOS V2 管理系统" |
88 | High |
| Service ad header | 搭建 二开 网站维护 on app modules |
content:"搭建 二开 网站维护" |
39 | High |
| DarkSword API surface | /api/ds/* beacon, result, war |
content:"/api/ds/" |
12, on 4 hosts | Medium |
The documents and the router carried out four indicators that the incident's public reporting
did not list: we.xpjkk[.]xyz and its resolution 43.247.132[.]175, read from the pentest
report; i.131422[.]com, the capture source in the router header; and the operator handle
JackApple. The IP address does appear in public reporting on an unrelated topic; the two
domains and the handle were not found in public reporting online.
Each is a lead for a saved search alert. The directory's files also referenced a cluster of
further hosts worth watching rather than treating as confirmed, including
k.ycka[.]my, t.ycka[.]my, load.msxf[.]info, io7krjae[.]cfd, strdanalysis[.]bond,
23.251.32[.]29 and 199.68.217[.]220. These were surfaced in the same workspace but not
independently profiled, so they are carried into monitoring at low confidence.
The YARA rules from this hunt run in Etugen's YARA scanning over files collected from open directories. They key on the distinctive kit artifacts rather than generic strings. The router rule is short and specific:
rule coruna_darksword_router_py
{
    strings:
        $a = "DarkSword" ascii wide
        $b = "/gooll/" ascii
        $c = "iOS 18 only" ascii wide
        $d = "131422.com" ascii
    condition:
        $a and 2 of ($b, $c, $d)   // router header plus a kit route or the capture source
}
Companion rules match CorunaParse.php on its WALLET_LETTERS map, DarkSword.php on its
/api/ds/ surface, the iOS V2 管理系统 operator banner, and coruna_bin.py on the
MASTER_KEY album packager.
The payload host, as Etugen recorded it
The injection side did reach Etugen, one day after the incident. On November 17, 2026, between
10:16 and 10:27 UTC, Etugen recorded 136.113.106[.]136, the address public reporting gives for
the payload domain 1688360[.]cc. The host sits in AS396982, Google LLC, in the United States,
with ports 22, 80, 443, 20201 and 20202 open (port 22 had been on record since May 16, 2026) and an nginx 1.24.0 server on Ubuntu that redirects
plain HTTP to www.1688360[.]cc. Etugen's catalog labels it CryptoClipper and DarkSword,
severity high, confidence 85.
Its Trashpile holds five distinct files collected from port 443, seven records in all because
track.js and go.js were collected under both the root https://1688360[.]cc/ and the bare IP.
| File | Size | SHA-256 | Collected, UTC |
|---|---|---|---|
track.js |
29,882 B | f7b84b9a94f749f8ced3f0112d0a66894e8bbc3b4aa5592021d1b8976a9bad40 |
2026-11-17 10:16 |
go.js |
2,230 B | 619d5522e6a7de1f7a985a73f8cb569752edc84153878e20f35bf3d8b12079c6 |
2026-11-17 10:20 |
landing.html |
12,572 B | 749ed9f8c8f0114aa65f4ed786c0513e9b5ffc82e13134b12f73e6ef5a5c6def |
2026-11-17 10:22 |
shell-guard.js |
3,398 B | 483005a8327e599037c6891fbafa425563c9d906e4fb95395fab47bdd8dfc79a |
2026-11-17 10:23 |
html2canvas.min.js |
198,689 B | e87e550794322e574a1fda0c1549a3c70dae5a93d9113417a429016838eab8cb |
2026-11-17 10:24 |
Three things stand out. The track.js hash is one of the builds listed in public reporting, so
Etugen collected the reported payload from the server itself. The server was still answering on
its IP ten hours after public reporting says the domain was suspended at the registry. And three
of the file names, go.js, landing.html and shell-guard.js, do not appear in the public
indicator lists at all. The two addresses published for the iOS router domains were not found in
Etugen.
What the files are
The files were read from Etugen's copies, not from the live server.
| File | What it is | Indicators inside |
|---|---|---|
track.js |
The payload served to injected sites. 716 lines, not obfuscated, comments in English | 1688360[.]cc/hit.php, 1688360[.]cc/card.php, 1688360[.]cc/html2canvas.min.js, 5vobauua3ojpklx[.]icu/boot.js, eil786npto9u5bq[.]icu/boot.js, eil786npto9u5bq[.]icu/JIUJIU888/weifile.html, eight replacement wallet addresses |
landing.html |
A product landing page styled after a hardware wallet brand, comments in Chinese | 5vobauua3ojpklx[.]icu/embed.js?ch=877d0432&k=4d18c0aadaf93bf9, and a reference to /track.js |
go.js |
Sends clicks on a cloned home page to landing.html, comments in Chinese |
landing.html |
shell-guard.js |
Keeps a cloned page as a static shell: links, forms and off-site requests are neutralised, comments in Chinese | attribute data-shell-guard |
html2canvas.min.js |
A copy of a public screenshot library | none |
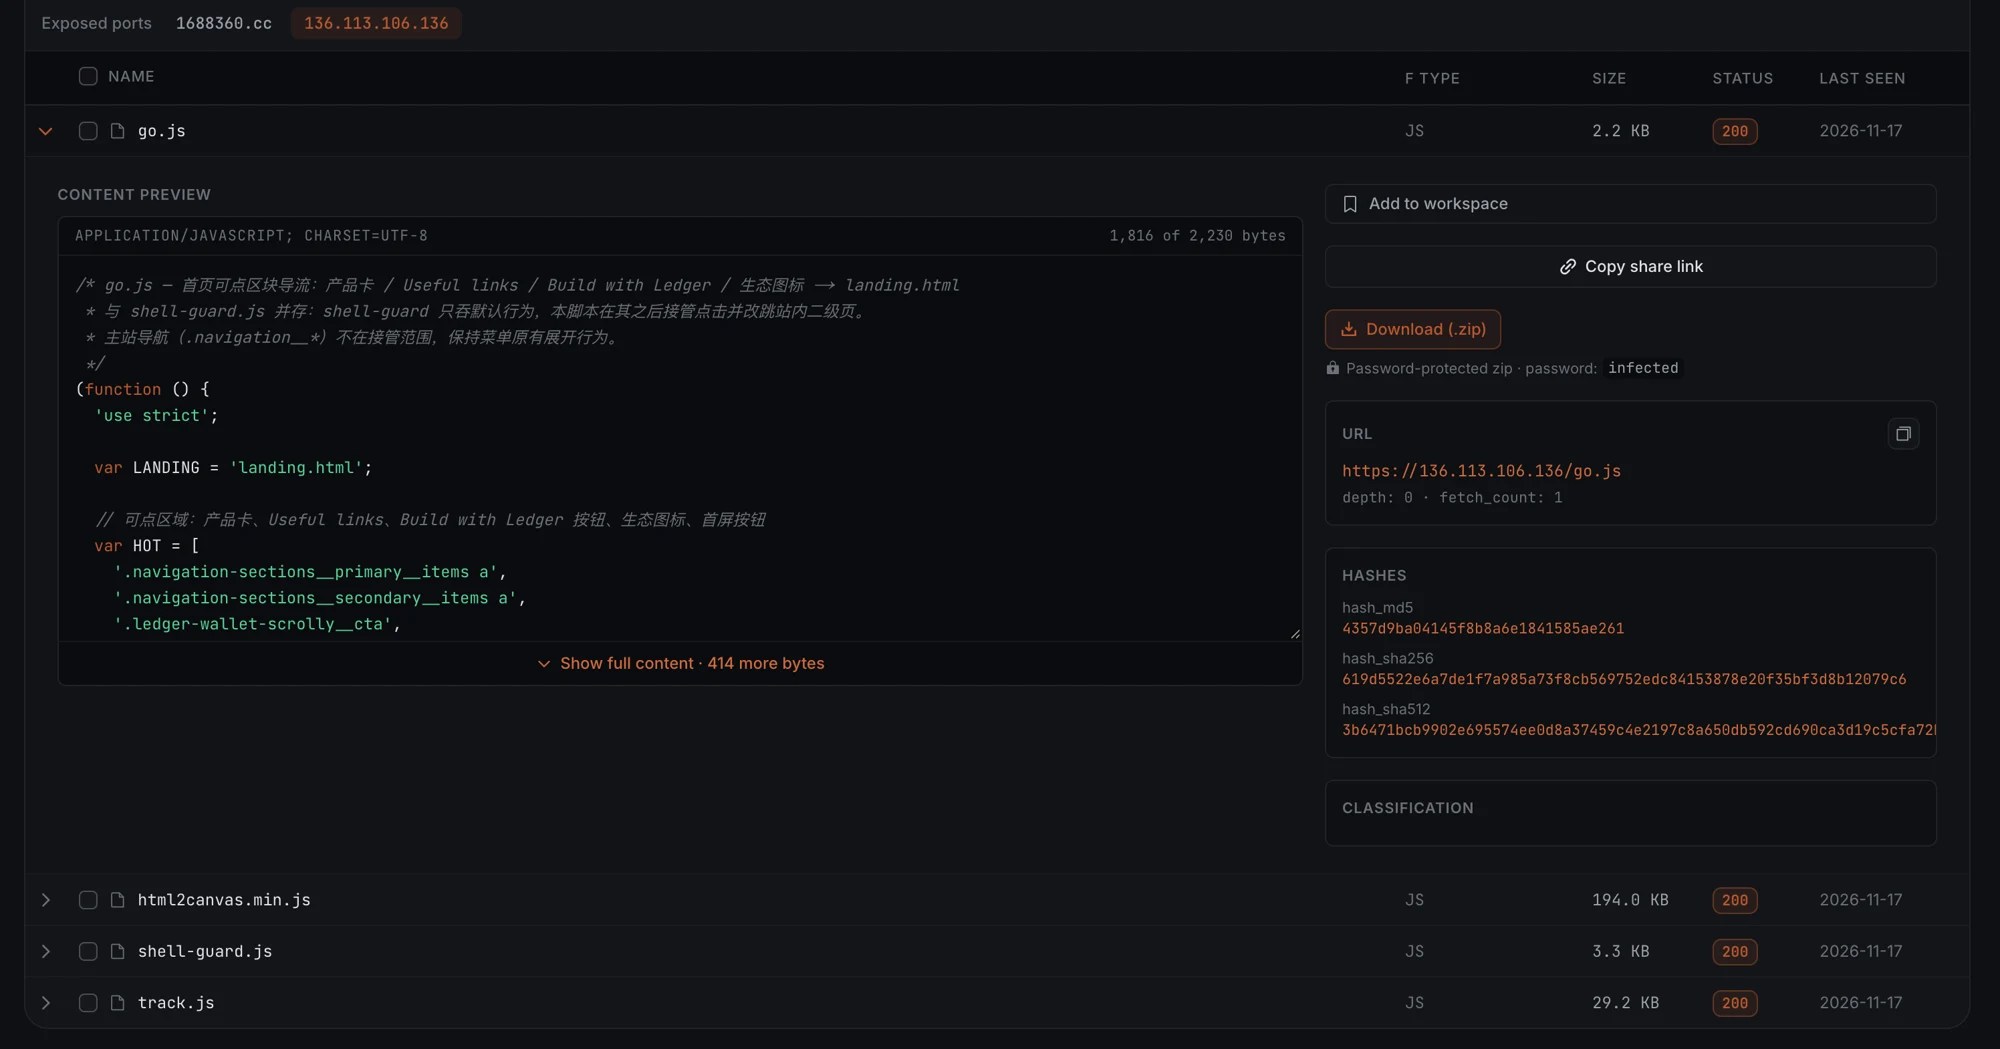
The copy of track.js confirms the published picture from Etugen's own data: both router
domains, both collection endpoints and the eight wallet addresses are in the file. It also adds
to it. The router path /JIUJIU888/weifile.html, the script embed.js with its channel
parameter ch=877d0432, and the three files that turn the payload host into a cloned storefront
for a wallet brand are not in the public indicator lists. So the same server that fed the
injected snippets was also set up as a lure site of its own.
Where the payload meets the kit
This is the link the first half of this post could not make. Two artifacts in the incident's payload are specific to the kit family that Etugen had already indexed.
Artifact in the incident's track.js |
Where else Etugen has it | Etugen query | Files |
|---|---|---|---|
Attribute data-chain-url, set on the boot.js script tag |
boot.js on 104.233.217[.]108, collected November 1 and 2, which reads that attribute |
content:"data-chain-url" |
5 |
Stage directory weifile under a channel directory |
104.233.217[.]108, where the kit's channel_defaults.json sets it as the stage directory under channel/<name>/, and on 31.58.136[.]212, 14.128.50[.]213 and 14.128.50[.]253 |
content:"weifile" |
27 |
data-chain-url occurs in five files across all of Etugen: the payload on the incident's host
and the router script in the workbench, nothing else. The incident's loader passes its settings
to boot.js through the same attributes the workbench's boot.js reads, and it points at a
weifile stage under a channel directory named JIUJIU888, the layout the kit's own defaults
describe. On that evidence the iOS stage of the incident was built with this kit family, with
high confidence.
Who ran it is a separate question. The published router domains and the channel code 02111110
are still absent from the workbench, so the incident was not run from that directory. The
channel name is the one lead: jiujiu888 is also the account name recorded in the workbench's
files about a fraud operation. A shared handle is a weak tie by itself and is carried here as a
lead, not as attribution.
The workbench also holds browser storage that records a further deployment using the same
layout, ssrgbkbky[.]com/channel/8.9.4J/weifile/, which was not found in public reporting
online.
The same kit on seven more hosts
The workbench is not the only place the two kit names appear. A filename search across all of
Etugen returned 36 files named for DarkSword and 63 named for Coruna, on six hosts besides
the seed. A seventh host, 31.58.136[.]212, carries no file with either name but holds iOS exploit
chain scripts whose content names DarkSword. None of these hosts was found in public reporting online.
| Address | What the Trashpile holds | Open port | First seen | Verification |
|---|---|---|---|---|
31.58.136[.]212 |
23,909 files, with iOS chain scripts that name DarkSword in their content, such as rce_loader.js and kernel_priv_26.js |
8899, 9002 | 2026-11-02 | Etugen Trashpile |
14.128.50[.]213 |
15,015 files, with DarkSword C2 and panel process logs | 8089/tcp | 2026-10-22 | Etugen Trashpile |
14.128.50[.]149 |
22,742 files, with DarkSword C2 and panel process logs | 8089/tcp | 2026-10-22 | Etugen Trashpile |
14.128.50[.]253 |
11,773 files, with DarkSword panel files | 8089/tcp | 2026-10-22 | Etugen Trashpile |
47.102.192[.]23 |
59,291 files, with Coruna analysis notes | 9094, 9876, 8888, 19877 | 2026-06-19 | Etugen Trashpile |
65.108.218[.]45 |
804 files, with one DarkSword-named page | 7777/tcp | 2026-06-20 | Etugen Trashpile |
172.245.39[.]245 |
851 files, with Coruna-named enumeration files | 9000/tcp | 2026-10-15 | Etugen Trashpile |
The dates matter. The earliest of these files reached Etugen on June 19, 2026, five months
before the incident, and the three hosts in 14.128.50[.]0/24, all in CTG Server Limited, were
indexed with process logs for a C2 and a panel on October 22. These hosts were profiled from
Trashpile metadata and file names; their files were not read in depth, so the role of each is
stated from what the names and counts show. As with the seed, none of the published incident
indicators was found on any of these seven hosts.
Tactics and techniques
The workbench was mapped against MITRE ATT&CK, yielding ten techniques across six tactics. The
ones confirmed firsthand rest on files read in the directory: the kit source itself as
capability development, the DarkSword HTTP C2 surface, the credential and wallet collection
modules, and the 7z album packager. The campaign-level techniques, supply-chain delivery,
drive-by compromise and DGA domain generation, are described by public reporting and the kit's
own routing but were not observed as live network activity from this host, so they are marked
confirmed: false.
Resource Development
Initial Access
Execution
- T1203Exploitation for Client Execution iOS 18 exploit chains, darksword_router.py and DarkSword.php
Credential Access
- T1552.001Unsecured Credentials: Credentials In Files darksword_passwords.txt, wallet mnemonic parsing
Collection
Confirmed from analysisSuspected, not confirmed
Detection and defense
| Layer | Recommendation |
|---|---|
| Network | Watch for 43.247.132[.]175, we.xpjkk[.]xyz and i.131422[.]com in egress and DNS, and save an Etugen search alert for the two domains |
| Network | Block webshell[.]lol with its subdomains chat.webshell[.]lol and xiaoshen.webshell[.]lol, and 1688360[.]cc |
| Network | Alert on DarkSword C2 shape /api/ds/beacon, /api/ds/result, /api/ds/war and the router routes /go/, /pe/, /gooll/ |
| Network | For the injection stage described in public reporting, block the reported .icu routers and the telemetry endpoint /api/iptj, which are separate from this workbench |
| Endpoint | Hunt for files named CorunaParse.php, DarkSword.php, darksword_router.py, coruna_bin.py and the coruna_*.py management scripts |
| Endpoint | Use the iOS V2 管理系统 operator banner and the 搭建 二开 网站维护 service-ad header as content signatures for cloned kit files |
| Identity | Treat any device that loaded a hidden iframe from the reported injectors as a wallet-theft exposure, since the collection modules parse wallet mnemonics and tag wallet sources |
| General | The password list and wallet material in the directory most likely belong to victims rather than the operator; route that collection, under masking, to the affected parties through the appropriate channel |
| General | Load this hunt's YARA rules into Etugen's YARA scanning and save a search alert for the handle JackApple |
Takeaways
The first point is that an exposed directory can tell you which stage of a campaign you are looking at. The November 16 reporting mapped the injection side. This host is the back office: the kit parsed, rebuilt from captured traffic, maintained with audit and recovery scripts, and advertised as a buildout service. The content search that found none of the injection-side strings is what draws that line, and it is a line defenders can act on.
The second point is about what the kit is really after. The collection modules do not chase generic data. They parse wallet seed phrases, tag the wallet brand down to a single channel letter, and package photo albums into encrypted archives. A drive-by chain against iPhones and iPads, in this operator's hands, is a crypto-theft pipeline with a curated back office.
The third and final point is provenance. The router header records that the chain was captured
from a deployment at i.131422[.]com, and the operator report documents a break-in against a
JackApple admin panel at we.xpjkk[.]xyz. One actor is building on another's work and selling
the result. Those three addresses never appeared in the incident's public indicators, and they are the
thread a defender should pull next.
IOC list (defanged)
New infrastructure surfaced by Etugen from the workbench files:
| Type | Value |
|---|---|
| Domain | we.xpjkk[.]xyz |
| IPv4 | 43.247.132[.]175 |
| Domain | i.131422[.]com |
| Operator handle | JackApple |
| Service ad | 搭建 二开 网站维护 |
Open directory host:
| Type | Value |
|---|---|
| IPv4 | 104.233.217[.]108 |
| Port | 8888/tcp |
| ASN | AS54600, PEG TECH INC |
Payload host of the incident, as recorded by Etugen:
| Type | Value |
|---|---|
| IPv4 | 136.113.106[.]136 |
| Domain | 1688360[.]cc, www.1688360[.]cc |
| Ports | 22, 80, 443, 20201, 20202 |
| File names | track.js, go.js, landing.html, shell-guard.js, html2canvas.min.js |
Files collected by Etugen from the payload host (SHA-256):
New indicators read from the payload host files and the workbench:
| Type | Value |
|---|---|
| URL | 5vobauua3ojpklx[.]icu/embed.js?ch=877d0432&k=4d18c0aadaf93bf9 |
| URL | eil786npto9u5bq[.]icu/JIUJIU888/weifile.html |
| Domain | ssrgbkbky[.]com |
| Strings | data-chain-url, data-channel-code, data-landing, data-shell-guard, weifile |
Injector domain from public reporting, with the subdomains seen in stealer log records:
| Type | Value |
|---|---|
| Domain | webshell[.]lol |
| Domain | chat.webshell[.]lol |
| Domain | xiaoshen.webshell[.]lol |
| URL path | /get.js, /guest |
Further hosts carrying files named for the kits:
| Type | Value |
|---|---|
| IPv4 | 31.58.136[.]212 |
| IPv4 | 14.128.50[.]213 |
| IPv4 | 14.128.50[.]149 |
| IPv4 | 14.128.50[.]253 |
| IPv4 | 47.102.192[.]23 |
| IPv4 | 65.108.218[.]45 |
| IPv4 | 172.245.39[.]245 |
File hashes (SHA-256): reported track.js builds, injection stage per public reporting. The
second was collected by Etugen from the payload host; neither was found in the open directory.
| File | SHA-256 |
|---|---|
track.js build |
814a963c0da480e2449d9b6664480156e1cd6d731014117401bf635badec3a0f |
track.js build |
f7b84b9a94f749f8ced3f0112d0a66894e8bbc3b4aa5592021d1b8976a9bad40 |
Host-based indicators:
| Type | Value |
|---|---|
| Operator banner | iOS V2 管理系统 |
| Kit files | CorunaParse.php, DarkSword.php, darksword_router.py, coruna_bin.py |
| Router routes | /go/{code}, /pe/{filename}, /gooll/{filename} |
| DarkSword API | /api/ds/beacon, /api/ds/result, /api/ds/war |
| Coruna channel fields | /a, /u, /event, /ub, /uj, /us |
| Collection packager | coruna_bin.py, 7z archive with MASTER_KEY password |
References
The findings in this post rest on analysis of files found in a publicly exposed directory and on Etugen's scan and Trashpile data. Prior public reporting on the campaign is kept separate from what Etugen observed firsthand. All indicators were valid at the time of writing.